
Quick Start
This guide helps you log in and start using the TestNet platform in 5 minutes.
Step 1: One-Command Installation
Run the following command on your target Linux server (with Docker & Docker Compose installed). The script auto-detects the fastest mirror, downloads components, and completes deployment:
curl -fsSL https://cnb.cool/testnet0/testnet-public/-/git/raw/main/install.sh | bashAfter installation:
- The admin password and service secrets are auto-generated in the
.envfile;ADMIN_INIT_PASSWORDis the initial login password - Open
https://<server-address>:3100to access the platform
TIP
For full system requirements, offline installation, and parameters, see Setup & Activation.
Step 2: Log In to the System
Access the TestNet URL (default https://your-server:3100) and log in with the credentials provided by the administrator.
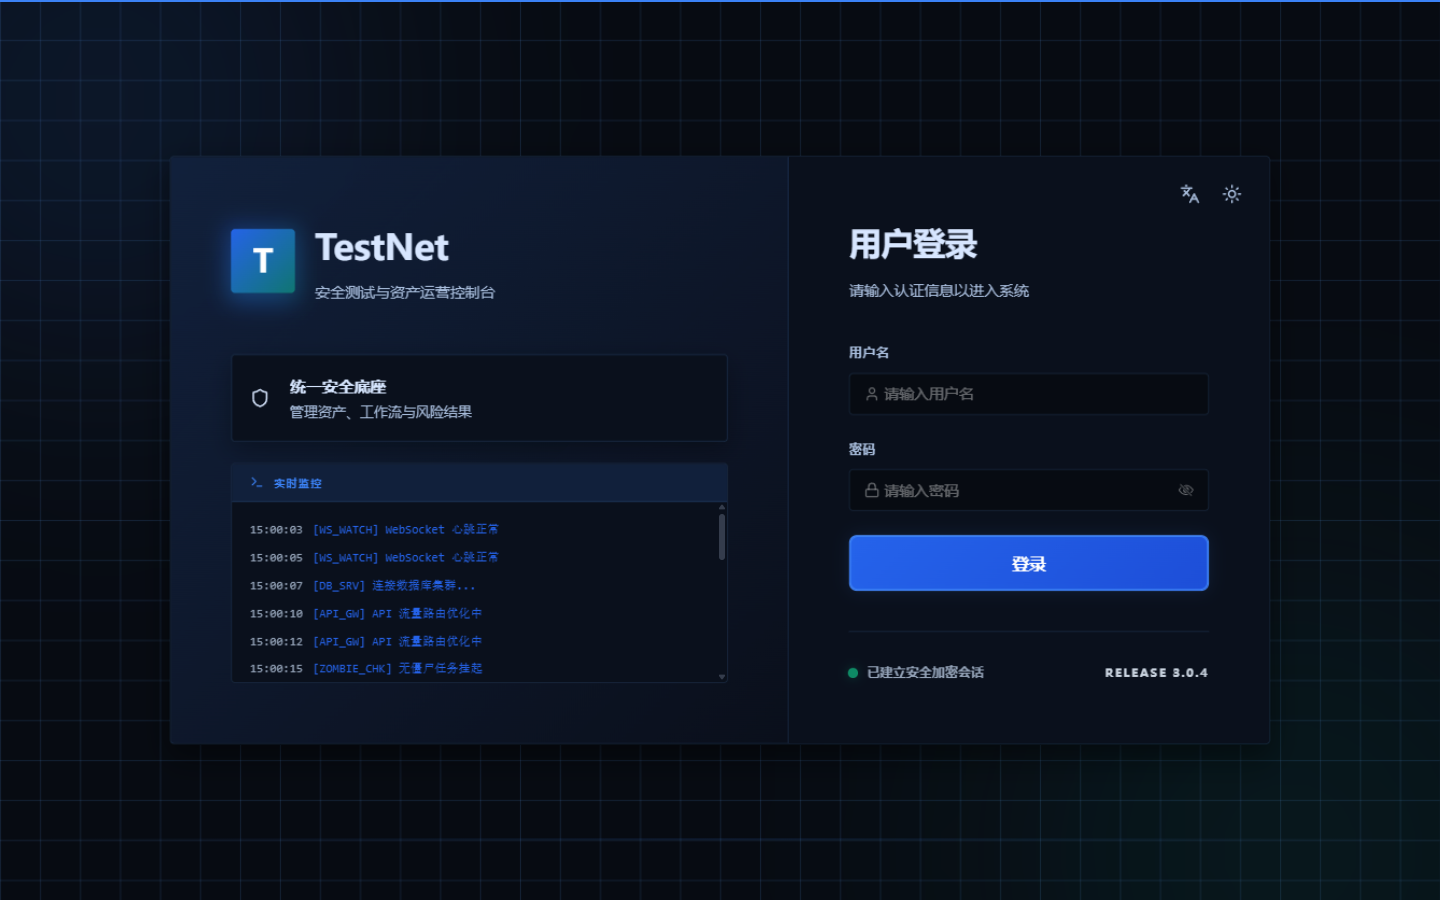
Default Credentials
- Username:
admin - Password: Automatically generated during deployment (check deployment logs or
ADMIN_INIT_PASSWORDin.env).
After Docker deployment, you can reset the password to Admin@123456 using ./testnet.sh reset-password.
Change Initial Password
- Click on the user profile icon in the top right corner.
- Select Profile Settings.
- Switch to the Security tab.
- Fill in your current password and new password.
- Click Save.
Main Modules
| Group | Module | Description |
|---|---|---|
| Core (CORE) | Dashboard | Real-time security posture metrics, recent task status, and operational charts. |
| Projects | Multi-project isolation and dedicated Project Workbench dashboards. | |
| Asset Management (ASSETS) | Asset Management | Lifecycle management, topology graph visualization, and filtering across 8 core asset models. |
| Asset Config | Configure tag management, ownership mappings, root-domain settings, access rules, notification linkage, vulnerability types, and retention cleanup. | |
| Information Collection (SECURITY) | Cyberspace Search | Multi-engine search (FOFA, Shodan, Hunter, Quake) with one-click asset batch ingestion. |
| Automation | Visual DAG workflow designer, security tool repository, config file distribution, and Run Center. | |
| Scan Nodes | Distributed probe registration, heartbeat monitoring, and health scheduling. | |
| AI (AI) | MCP Access | 14 core facade MCP tools and one-click integration for Claude Code / Cursor / Windsurf. |
| Skill Library | SKILL.md knowledge cards with 11 categories, enable toggles, and skills.zip export. | |
| Memory Library | Cross-session persistent AI memories (Markdown memos), scoped globally or per project. | |
| Engagements | Penetration testing assessments with complete AI decision log and reasoning chains. | |
| HTTP Records | Single-step HTTP probe relay, traffic audit, response diff, and HAR 1.2 export. | |
| Credentials | 6 credential types with automated BOLA/IDOR cross-role authorization testing. | |
| System (SYSTEM) | Message Center | Internal notifications with email and Webhook channels, event subscription rules, and dispatch history. |
| System Admin | User, role, department RBAC, granular permission tree, global system configuration, and RSA licensing. |
Step 3: Create Your First Project
A project serves as the logical scope for isolating assets and workflows:
- Click Project Management on the left menu.
- Click New Project.
- Fill in the project name and description.
- Click Save.
Once created, use the Project Switcher in the top navigation bar to select the active project context.
Step 4: Add Your First Asset
Add Manually
- Click Asset Management → Domain on the left sidebar.
- Click the Add button.
- Enter the domain (e.g.,
example.com). - Click OK to save.
Import in Bulk
- Click the Import button.
- Download the Excel template.
- Fill in the domains according to the template.
- Upload the file to complete the import.
Step 5: Install Tools and Run Scans
Install a Tool from the Store
- Go to Tool Management → Tool List.
- Click the Store button.
- Find the tool you need (e.g.,
Subfinder). - Click Install.
Install a Pre-configured Workflow
- Go to Workflows → Workflow List.
- Click the Store button.
- Find the workflow you need.
- Click Install.
Step 6: View Scan Results
- Open the Run Center to monitor running tasks; click Logs for live execution details.
- Discovered assets are deduplicated and saved automatically — review them in the matching Asset Management lists.
- For workflow runs, open "Workflow Management" → "Run History" to inspect batch-produced assets.
Next Steps
🎉 Congratulations!
You have completed the basic workflow. Now you can explore:
- Project Overview — Multi-project isolation and the project workbench.
- Asset Graph Models — Core entity definitions and automatic cascading resolution.
- Common Asset Operations — Filtering, batch actions, and Excel import/export.
- Workflow Automation — Orchestrate complex automated scanning workflows.
- Distributed Nodes & Security — Probe pool governance, tool whitelists, and sandbox policies.
- Cyberspace Search Integration — Configure credentials for FOFA, Shodan, Hunter, etc.
- Playbooks — Hands-on scenarios for asset mapping, 0-day response, and distributed probing.