
Credentials
During enterprise penetration testing or automated API audits, evaluating authenticated endpoints requires legitimate session credentials across multiple privilege levels (e.g., Administrator vs. Regular User). TestNet provides a dedicated Target Credential Hub that securely manages test account tokens, injects credentials into automated requests, and performs automated cross-role authorization matrix tests (BOLA / IDOR / BFLA).
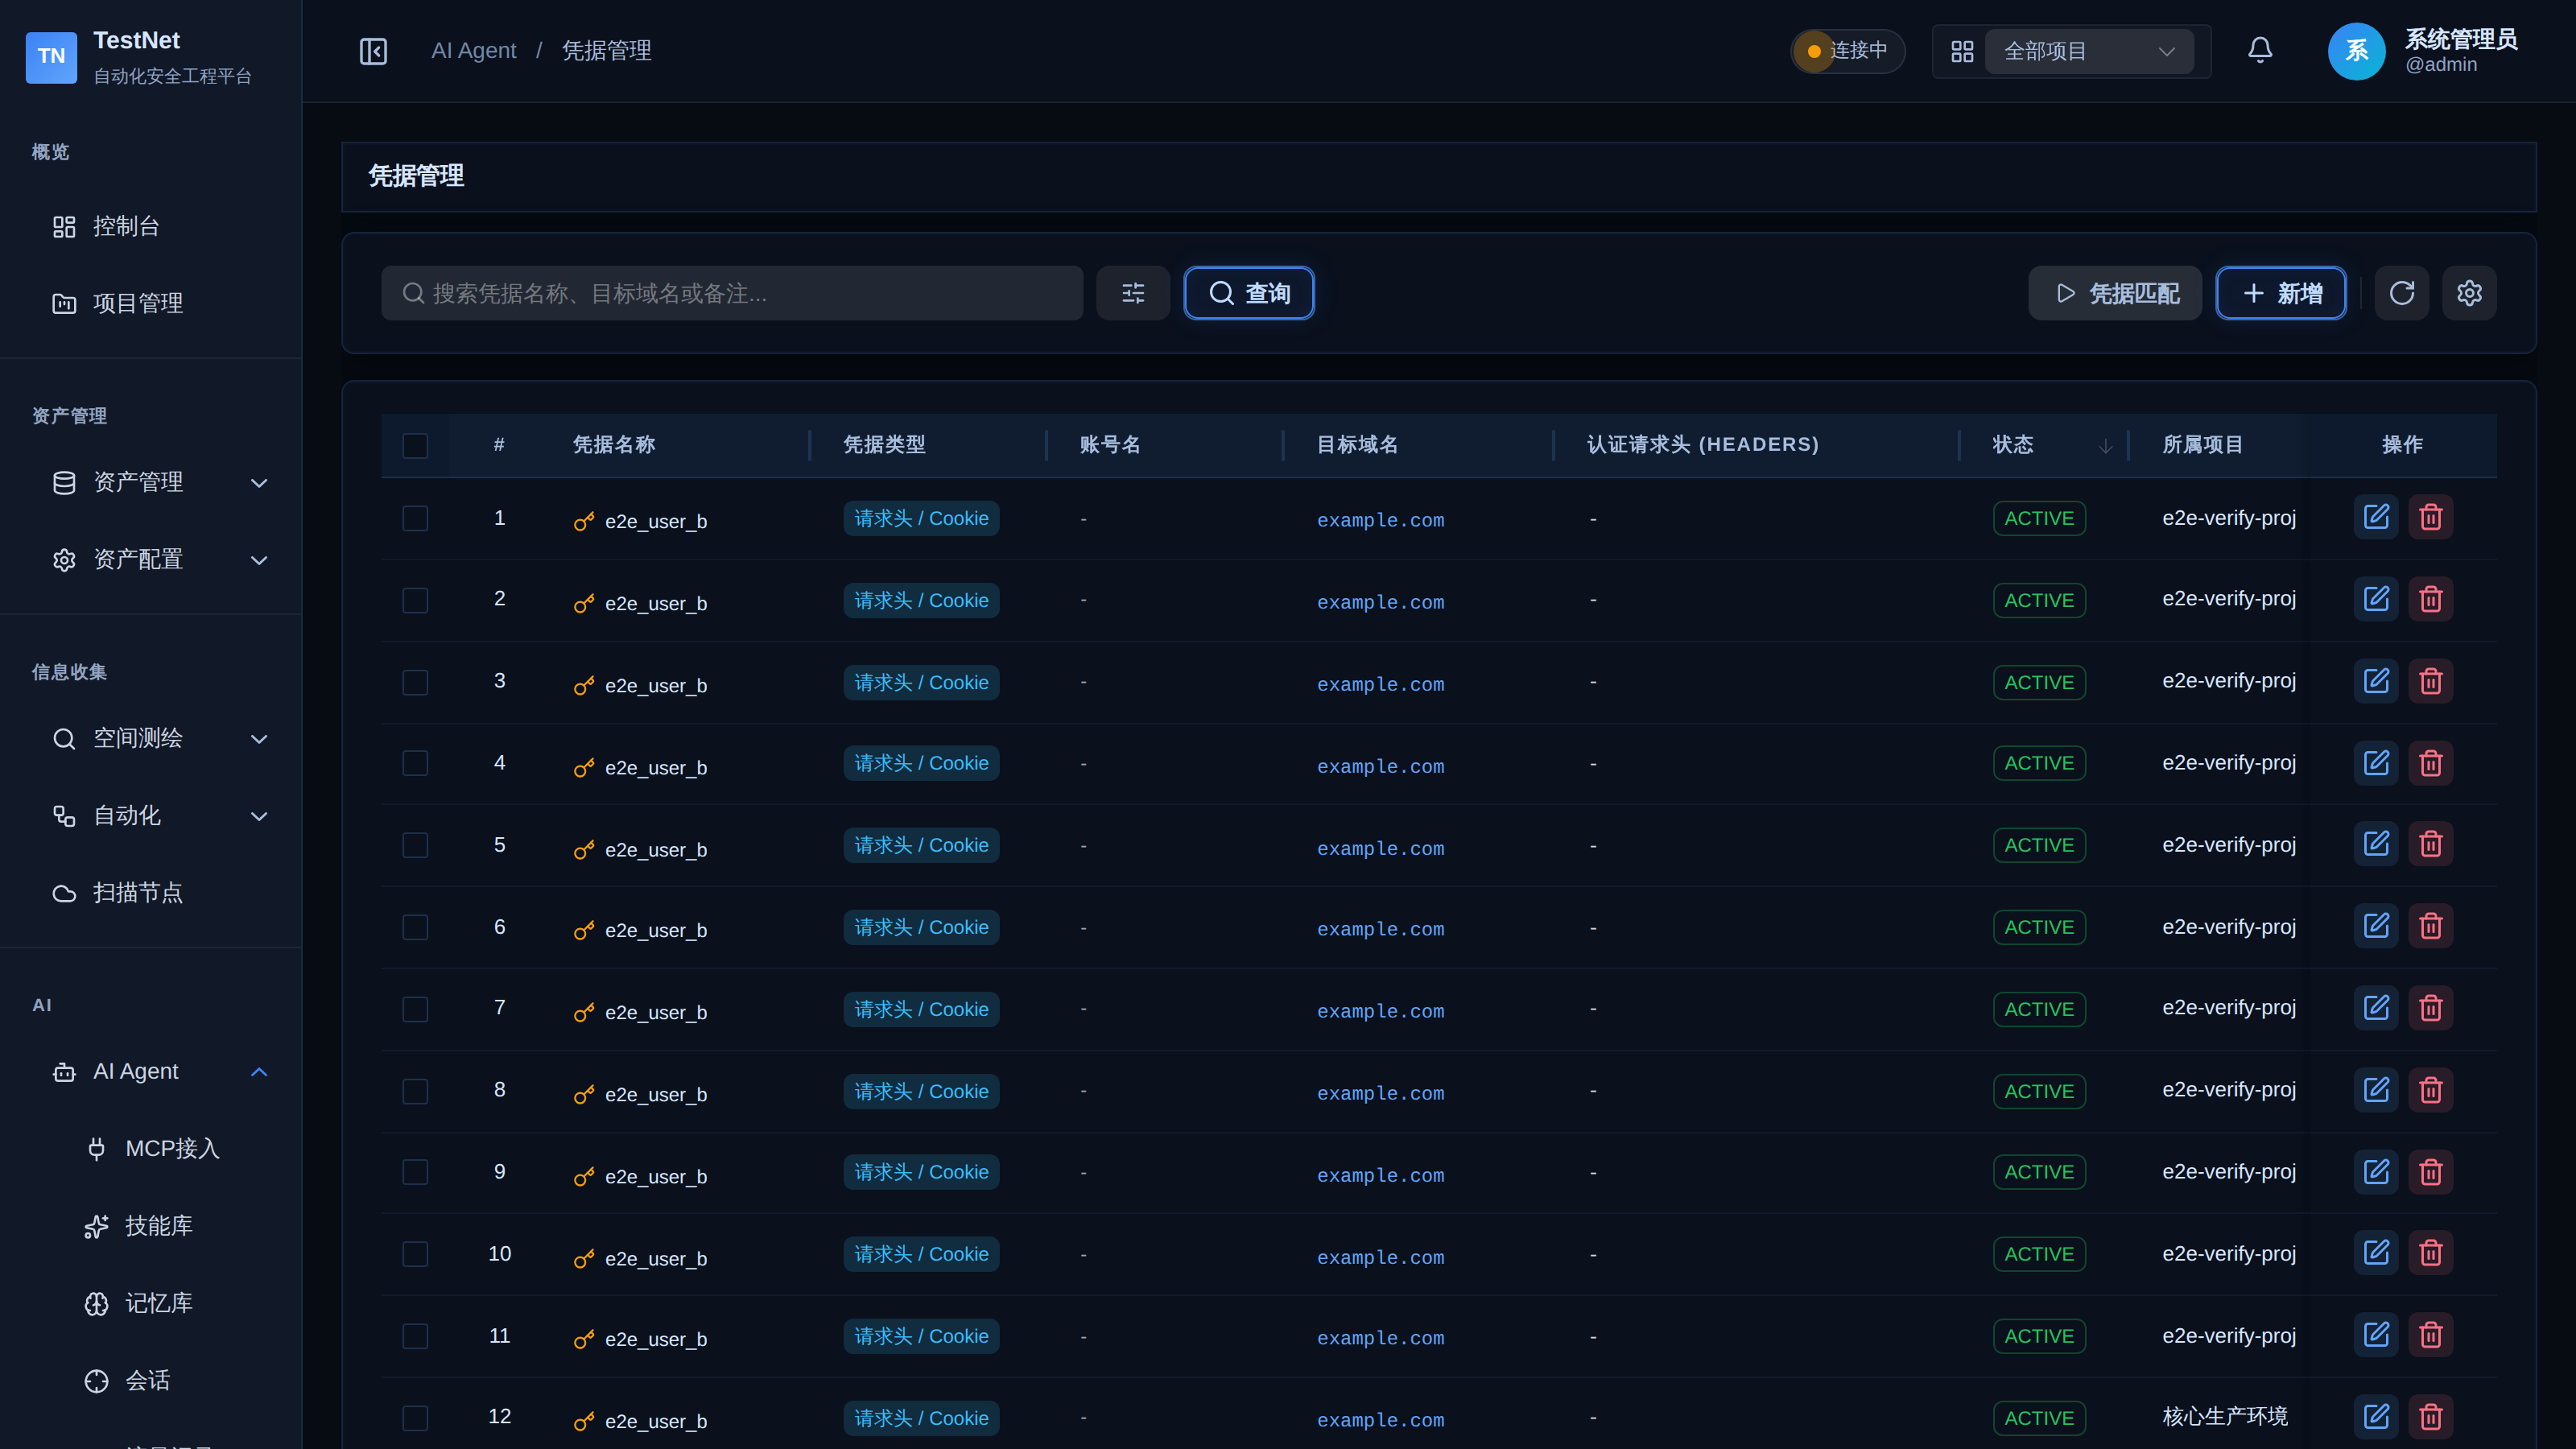
Supported Credential Types
TestNet natively supports 6 standard authentication protocols:
| Type | Injection Mechanism | Typical Use Case |
|---|---|---|
BASIC_AUTH | Authorization: Basic <base64> | Internal infrastructure, management routers, legacy devices |
BEARER | Authorization: Bearer <jwt_or_token> | Modern RESTful APIs, OAuth 2.0, JWT microservices |
TOKEN | Raw token stored, mounted via injection template | Generic token credentials (non-standard Bearer scenarios) |
COOKIE | Cookie: key1=val1; key2=val2 | Web SPAs, traditional Session-Cookie applications |
API_KEY | Custom Header (X-API-Key: xxx) or Query param | OpenAPI gateways, third-party developer integrations |
HEADER_MAP | Multiple custom header key-value pairs injected at once | Custom authorization proxies, multi-header scenarios |
Credential Management & Safe Injection
Navigate to "AI" → "Credentials" in the left sidebar.
1. Adding a Target Credential
Click "New" and configure:
- Credential Name: e.g.,
TenantA-StandardUserorTenantA-GlobalAdmin. - Project: Context project boundary (credentials are strictly scoped to prevent accidental cross-tenant testing).
- Target Host: e.g.,
api.target.com(enforces strict hostname binding so tokens are never leaked to external hosts). - Credential Form: The web form captures password-style (PASSWORD) / header-style (HEADERS) payload forms; the 6 protocol types are supported by the injection engine and the MCP
save_credaction. - Payload / Value: Enter the token, cookie string, or API key (masked automatically in the UI).
2. Header Stripping & Overwrite Engine
When dispatching requests via the HTTP relay, TestNet enforces two critical guarantees:
- Automatic Header Stripping (
stripAuthHeaders): Cleanses existingAuthorizationandCookieheaders from baseline payloads to eliminate unintended token contamination. - Dynamic Credential Injection (
replaceCredentialInHeaders): Injects the selected test role's credentials atomically, guaranteeing repeatable and precise test states.
Automated Access Control Matrix Testing (BOLA/IDOR)
Broken Object Level Authorization (BOLA) and Broken Function Level Authorization (BFLA) remain top OWASP API Security risks. TestNet turns access control testing into a turnkey automated pipeline:
Testing Procedure
- Prepare Credentials: Store at least two distinct user privilege levels in the credential vault (e.g., Admin vs. Normal User).
- Execute Test:
- Prompt the AI agent to invoke
testnet_access_control(action="matrix_test")(the matrix test is currently provided via the MCP interface; there is no dedicated web-UI entry); - You can also specify the target URL and test credential aliases manually in your MCP client.
- Prompt the AI agent to invoke
- Automated Assessment:
- The engine sends the request with baseline credentials, attacker credentials, and as an unauthenticated request.
- If the low-privilege attacker receives a
200 OKresponse with equivalent business payloads, TestNet flags a confirmed High-Severity BOLA/IDOR vulnerability with replication payloads attached.
Native MCP Tool Integration
External AI agents interact with the credential engine using these MCP facade calls:
// Example: testnet_access_control(action="matrix_test")
{
  "action": "matrix_test",
  "url": "https://api.target.com/user/profile",
  "method": "GET",
  "test_credentials": ["cred_admin", "cred_guest", "ANONYMOUS"]
}testnet_access_control(action="save_cred")(atomic nametestnet_save_target_credential): Store tokens discovered during active reconnaissance.testnet_access_control(action="list_creds")(atomic nametestnet_list_target_credentials): Query available test credentials by host and project (metadata only, no plaintext).testnet_access_control(action="matrix_test")(atomic nametestnet_test_access_control): Launch original/low-privilege/anonymous multi-identity authorization matrix comparison.
Related Documentation
- Engagements — organize testing progress and decision chains per engagement
- HTTP Relay & Audit — request tracing and response diffing after credential injection
- MCP Overview — how AI Agents connect to TestNet